mirror of
https://github.com/coder/coder.git
synced 2026-11-22 11:28:40 +08:00
feea5ab959f59cd2135443ed2a0c19bf7643db8f
17939
Commits
| Author | SHA1 | Message | Date | |
|---|---|---|---|---|
 Ethan |
feea5ab959 |
feat: add GPT-6.2 Astra and GPT-6.2 Sol to Agents and AI Gateway (#32370)
Closes CODAGT-1608 This adds `gpt-6.2-astra` and `gpt-6.2-sol` to the Agents known models catalog, so they're suggested when an admin adds a chat model, and regenerates the AI Gateway price book from models.dev so the gateway can price them. | Model | Input | Output | Cache read | Cache write | |---|---|---|---|---| | GPT-6.2 Astra | $8 | $40 | $0.40 | $10 | | GPT-6.2 Sol | $2 | $10 | $0.10 | $2.50 | Prices are per 1M tokens, and both models have a 1,050,000 token context window and 128,000 max output tokens. They're in the catalog for OpenAI (with a suggested effort of `medium`, same as `gpt-6-astra` and `gpt-6.1-sol`), OpenRouter and Vercel. models.dev doesn't list them on Azure or Bedrock yet, so I've left those out for now. Both models also reject the `none` and `minimal` reasoning efforts. A model config only sets a default and a maximum effort, so the picker always offers both, and picking either one fails the turn: ``` Unsupported value: 'none' is not supported with the 'gpt-6.2-astra' model. Supported values are: 'low', 'medium', 'high', 'xhigh', and 'max'. ``` We already send `low` instead for `gpt-6-astra` and `gpt-6.1-sol`, so to fix, we'll just do the same for the two new models. All four now live in one list of model ID prefixes, rather than a helper each. I checked this against the real models: all four return a 400 like the one above for `none` and `minimal`, and accept `low`. `gpt-6-sol` and `gpt-6.1-terra` still accept `none`, so they're left alone. Regenerating the price book also brings in everything else models.dev changed since the last weekly refresh, mostly on OpenRouter and Vercel: 22 other new entries (4 of them `-pro` and `-fast` variants of these two), 29 it dropped and 51 price changes. 6 existing catalog entries get new prices or limits the same way. |
||
|
Dean Sheather
|
7022f3f3b4 |
ci: pin wingetcreate in publish-winget and check its SHA-256 (#32387)
Pins the `wingetcreate.exe` that `publish-winget` downloads and checks its SHA-256 before running it. The job runs in the `release-publish` environment with cdrci's token, so it shouldn't run whatever `aka.ms/wingetcreate/latest` currently points at. ## Changes (`.github/workflows/release.yaml`, `publish-winget` job) - Downloads `wingetcreate.exe` from the GitHub release `v1.28.1.0` of microsoft/winget-create, not `https://aka.ms/wingetcreate/latest`. - Fails if the file's SHA-256 isn't `63d980ba79e97042395bd6eb5992c2db9e01e9e7a8a22958a95c288f27310413`, and deletes the file. - Keeps the output path `.\wingetcreate.exe`, so the next step doesn't change. - To upgrade, change `WINGETCREATE_VERSION` and `WINGETCREATE_SHA256` together. The comment above the step says where to find both. ## Where the hash comes from - **Same build as now:** `aka.ms/wingetcreate/latest` currently redirects to `releases/download/v1.28.1.0/wingetcreate.exe`, so releases already use this binary. - **Three sources agree on the hash:** - my own download; - GitHub's asset digest for `wingetcreate.exe`; - the `wingetcreate.exe.txt` checksum file Microsoft publishes in the same release. - **Signature:** the binary carries a Microsoft Authenticode signature. coder/coder-desktop-windows#196 pins the same version and hash. ## Checks - `actionlint .github/workflows/release.yaml`: clean. - `zizmor --offline .github/workflows/release.yaml`: no errors or warnings, on `main` or on this branch. --- AI disclosure: an AI coding agent (Xum) wrote this change and ran the checks above at my direction. It stays a draft until I've reviewed it. |
||
|
Thomas KosiewskiandJaayden Halko
|
8114ecdf47 |
feat(site/src/pages/AgentsPage/components): add the overview card container (#31590)
Adds `ChatOverviewCard`, the container that builds the overview card's data and renders `ChatOverviewCardView` from #31409. Nothing mounts it yet, so this PR changes no page. #31412 mounts it in the chat. The container reads the chat cost query, the git watcher's repositories, the pull request statuses, the subagent statuses, and the attachments from `useChatAttachments` (#31411). `getOverviewCost` turns the cost query into the card's three cost states. When the earlier attachments fail to load, the container passes the request to the view. Attachments then shows the same one-line "Failed to get attachments" alert with a **Retry** button as the Summary panel. I split this PR out of #31412 when that PR grew past 600 changed lines. The code is the same container that #31412 reviewed before, without the top bar toggle, which stays in #31412 with its only caller. | `Default` | `EarlierAttachmentsError` | |---|---| | 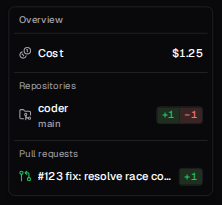 | 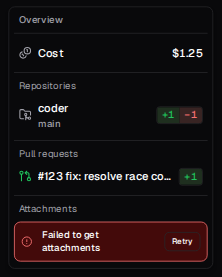 | ## How to test 1. Open Storybook at `pages/AgentsPage/ChatOverviewCard`, stories `Default` and `EarlierAttachmentsError`. 2. Run `pnpm test src/pages/AgentsPage/components/ChatOverviewCard.test.tsx` in `site/`. The page test in #31412 checks that **Retry** requests the earlier attachments again. ## What to look at first 1. `ChatOverviewCard`: one place builds the `ChatOverview` model from the queries and the chat store. 2. `getOverviewCost`: a failed refetch keeps the cost that loaded, and a chat without AI Gateway requests has no cost row. <details> <summary>Review history</summary> This container was reviewed as part of #31412 through three frontend-deep-review rounds, a code quality review, a polish pass, and a final review round. It moved here in the follow-up pass that fixed the open follow-ups: - The container now passes `earlierAttachmentsRequest` to the view, so a failed request shows its error and a retry. - `GitPanel/gitViews.ts` exports `countRepoChanges` here, where its first caller arrives. - Each repository row gets its `name` from `repoLabel(root)` and its trimmed `branch`, which the view shows as the subtitle, or "No branch" when it is empty. - The stories are new. They give the container's error state a screenshot. The stories have no `play` assertions, because the page test in #31412 covers the retry request. After #31411 merged, this branch was rebased onto `main` with no conflicts and now targets `main`. It picks up the smaller `AttachmentsErrorAlert` from #31411 without code changes here, so the screenshots above are new. </details> --- _Generated with [`xum`](https://github.com/coder/xum) • Model: `anthropic:claude-opus-5-5` • Thinking: `high`_ --------- Co-authored-by: Jaayden Halko <jaayden.halko@gmail.com> |
||
|
christin
|
62672563e3 |
fix(site/src): use green-500 for dark theme success tokens (#32046)
Fixes DEQ-172 (WCAG 1.4.3 Contrast (Minimum)) on the AI Gateway session threads page. In the dark theme, "Agentic loop completed" and "Session completed" use `text-content-success` (`#16A249`), which axe Auditor measured at 4.46:1 against `#27272A`. This moves the two dark theme success tokens that used green-600 (`142 76% 36%`), `--content-success` and `--border-success`, to green-500 (`142 71% 45%`, `#22C55E`). The dark theme already uses that green for `--git-added-bright` and `--chart-success-border`, and success text and borders stay the same green. | Background | Before (`#16A249`) | After (`#22C55E`) | |---|---|---| | `surface-primary` `#09090B` | 5.94 | 8.66 | | `surface-secondary` `#18181B` | 5.29 | 7.71 | | `surface-tertiary` `#27272A` | 4.45 | 6.48 | | `surface-green` | 4.45 | 6.49 | These tokens are global, so every dark theme success color gets slightly brighter. That covers success text, fills, and borders, for example health checks, `LastSeen`, toasts, status indicators, agent status borders, and template builder steps. This is intended: it lifts all success text above 4.5:1 rather than patching one page. Not changed: - Light theme: `--content-success` is green-700 and `--border-success` is green-600. Green-500 is 2.3:1 on white, which would fail 1.4.3 for text and 1.4.11 for borders. - Colorblind themes: they override these tokens with their own values. | | Before | After | |---|---|---| | Success text (`SessionTimeline/SecondThreadLoopOpen`) | 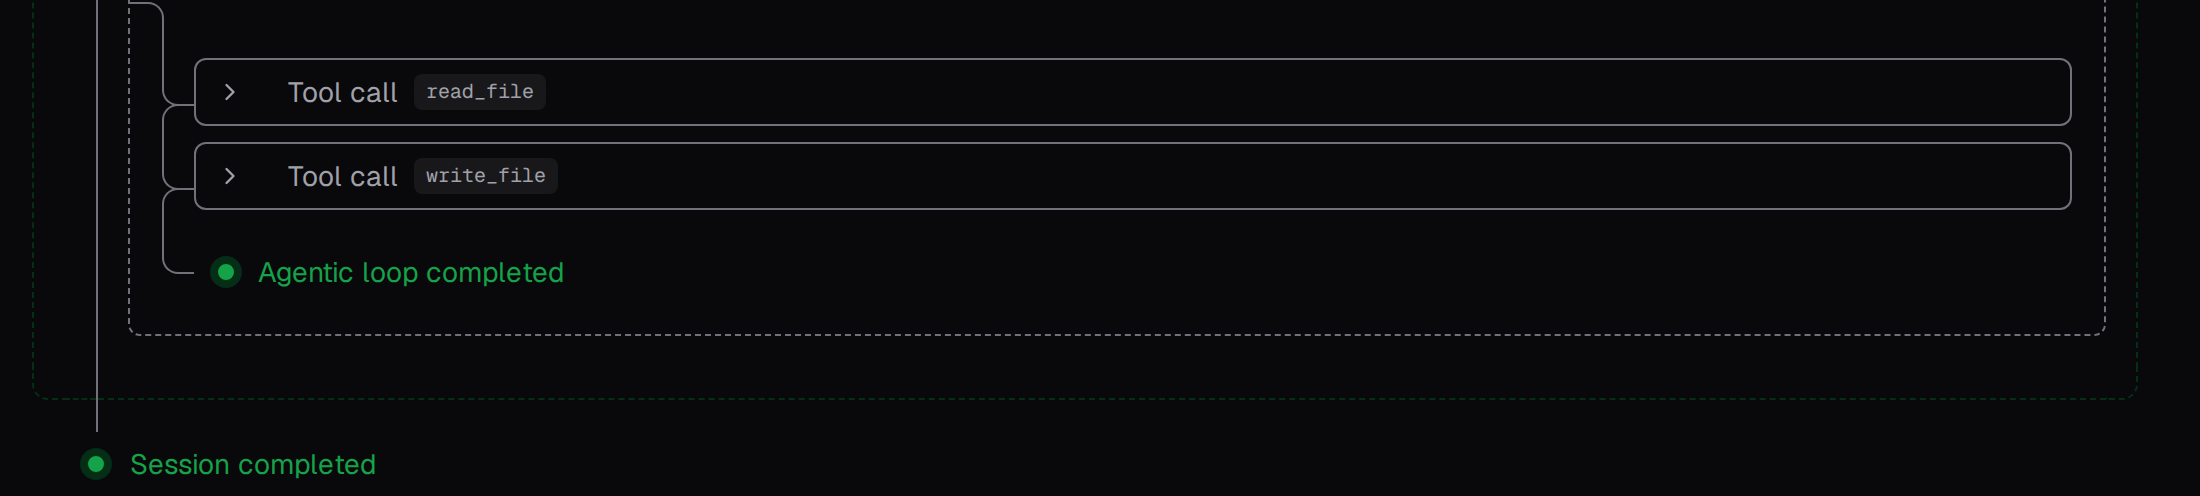 | 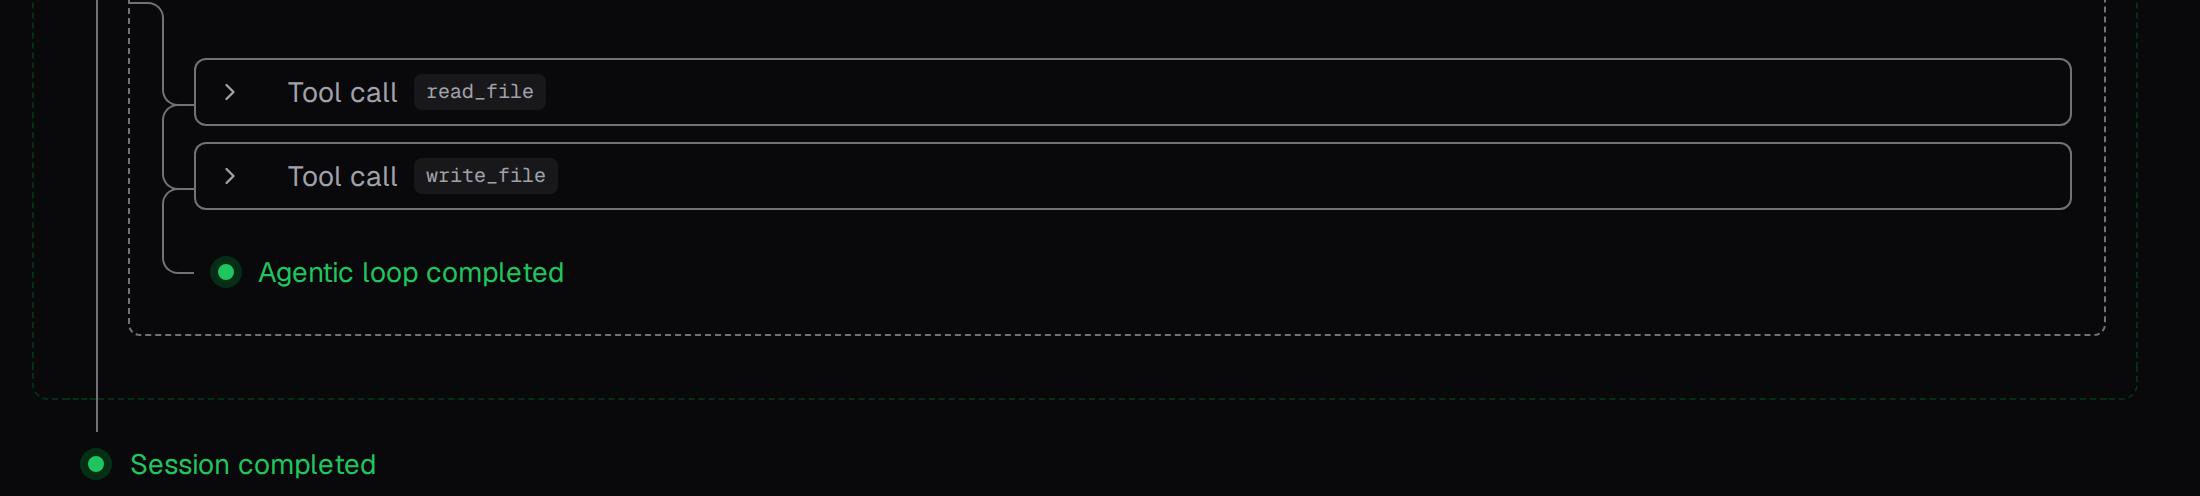 | | Success border (`SelectionSummary/WithModules`) | 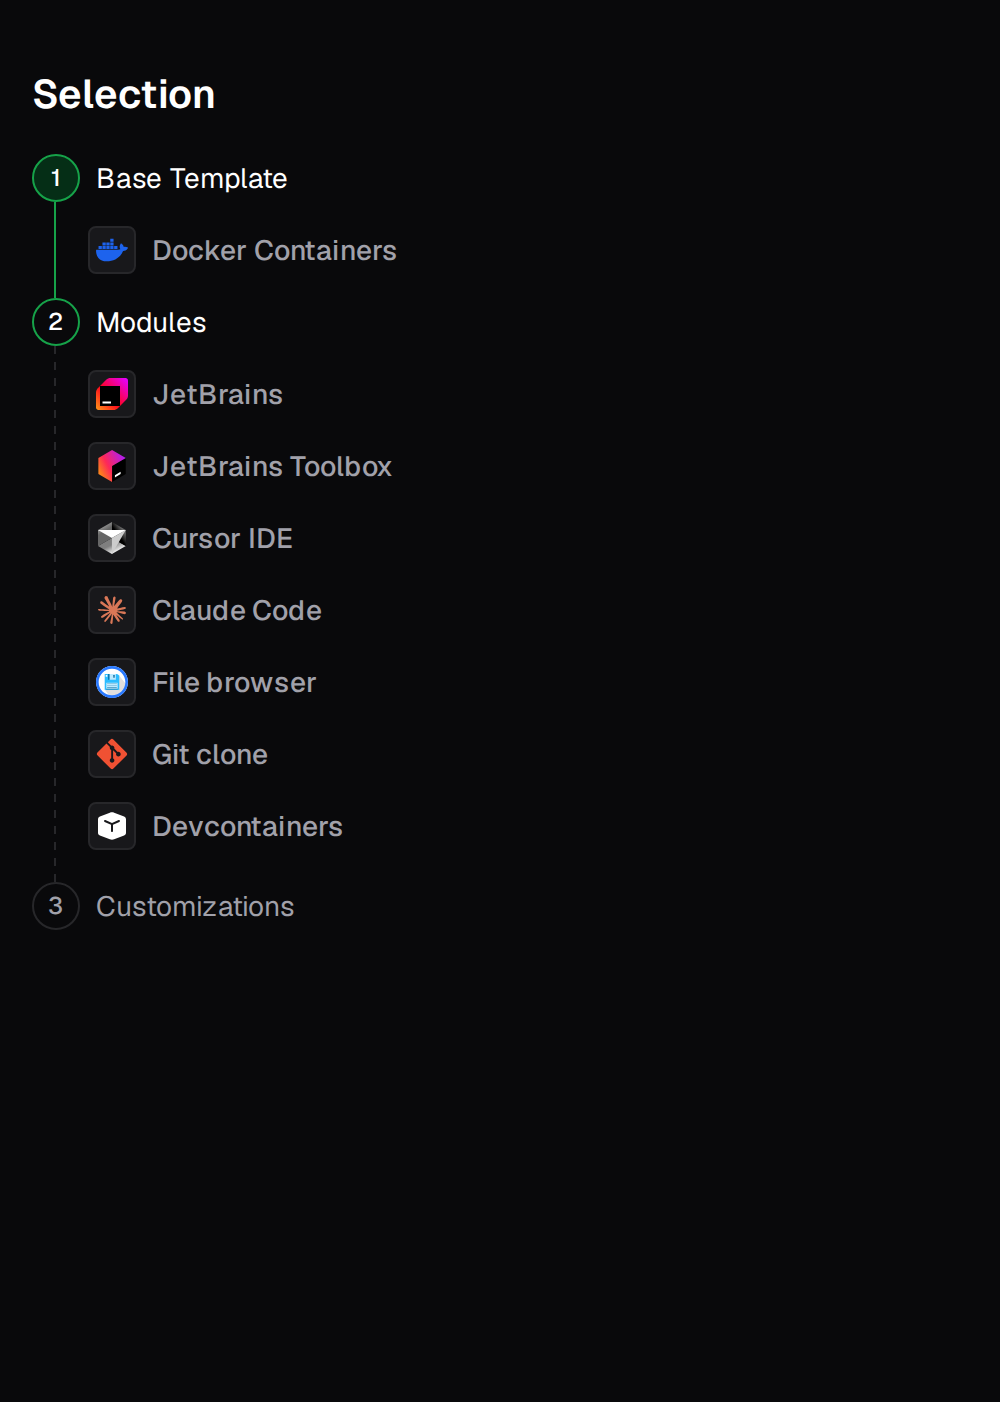 | 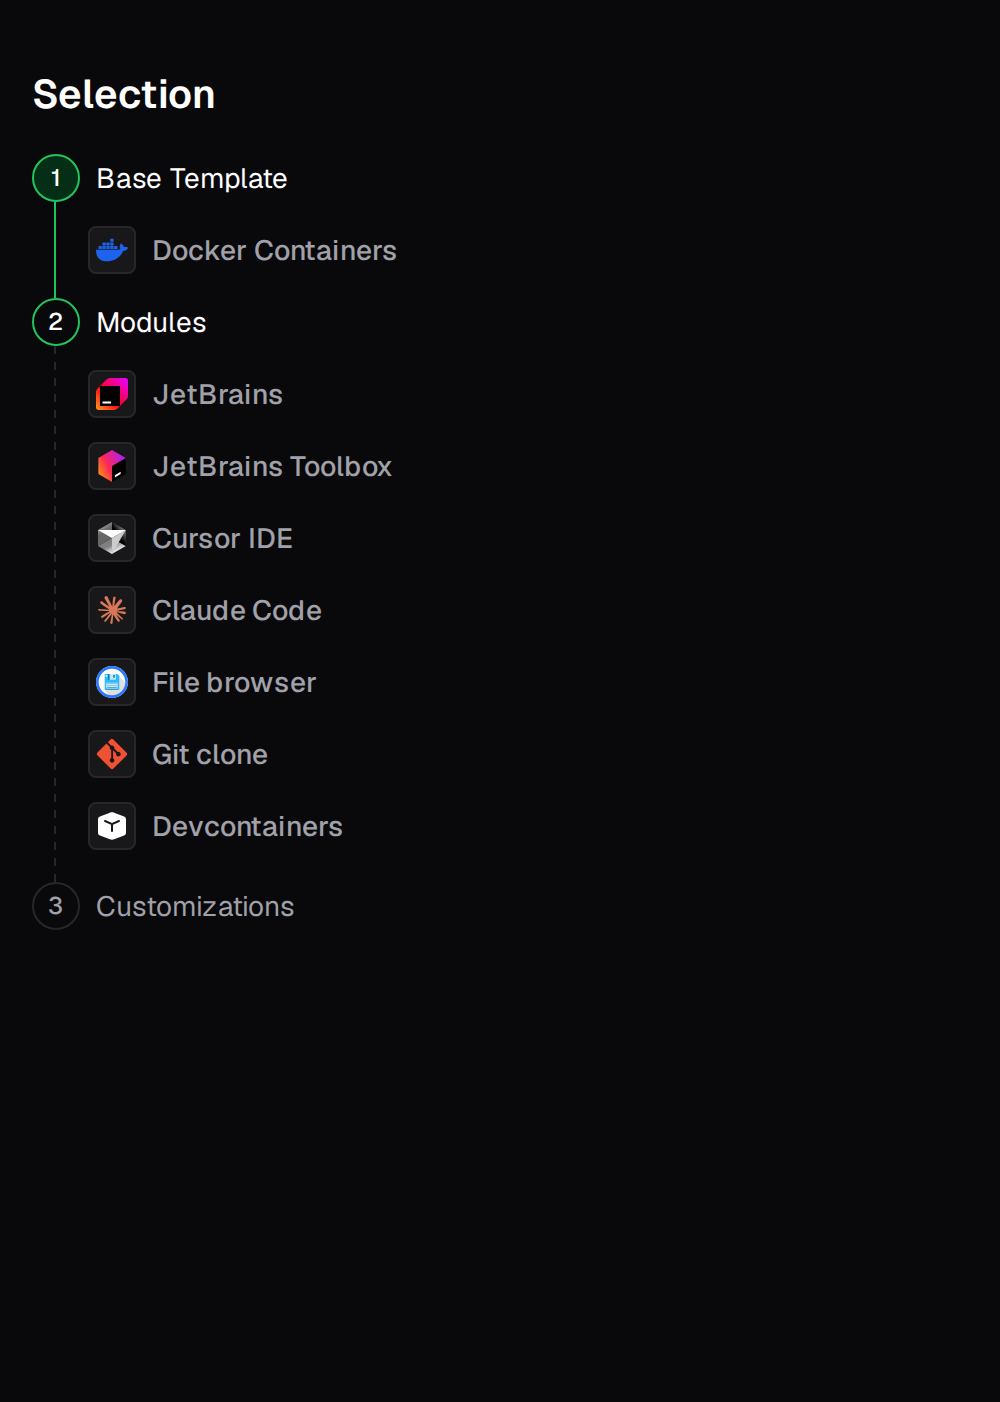 | Screenshots: Storybook, dark theme. > Generated by Coder Agents on behalf of @chrifro. |
||
|
Danielle Maywood
|
4c65d2c1a2 | fix(site): remove border from agent diff file tree (#32382) | ||
|
|
7c7e2e73cf |
feat: honor disable-model-invocation in uploaded skill content (#31159)
Addresses @ethanndickson's [review comment on #30882](https://github.com/coder/coder/pull/30882#discussion_r4344815088): the same `SKILL.md` file could be manual-only in Claude Code and the project dialog but automatic in Coder, because the server and the browser each handled `disable-model-invocation` in their own way. The server now owns the key for personal, organization, and project skills: - When a create or update request leaves `model_invocable` unset, `disable-model-invocation: true` in the content turns automatic use off, and `false` turns it back on. The key is read with the function workspace skills use, so a file gets the same setting in both places. Only YAML booleans count, so a quoted `"true"` is ignored. - An explicit `model_invocable` in the request always wins. - New content without the key leaves the setting unchanged, so editing text never turns it back on. - Content is stored as uploaded. Every API response returns content whose key agrees with `model_invocable`: when the stored file says otherwise, the server replaces the value of the key or adds the key before the first one, and leaves every other byte alone. - **Download** and **Export all** save the content the API returns, so the browser no longer edits the file. `withDisabledModelInvocation` is removed. - An upload is rejected with a 400 when the key holds a value the server can't replace with a boolean, such as a list. A later change to `model_invocable` can then always reach the file. Two edges: - Adding the key makes the returned file about 30 bytes larger, so a file at the 64 KB upload limit can be too large to upload again. - A skill stored before the upload check with a value the server can't replace is returned as stored. Workspace skills already honor the key since #31147. #31160, the frontend PR on top of this one, adds the switch to the personal and organization skill editors. > Generated by an agent on behalf of the user --------- Co-authored-by: Cursor <cursoragent@cursor.com> Co-authored-by: Nick Vigilante <nickvigilante@users.noreply.github.com> |
||
|
Jaayden HalkoandJake Howell
|
d1a58b9f5d |
feat: add script to check for title case (#21484)
Historically, much of the UI used title case. This PR adds a lint check
that reports title case UI text so it can be converted to sentence case,
and converts the existing text.
- `site/scripts/check-sentence-case.mjs` runs as `pnpm
lint:sentence-case` and is part of `pnpm lint`. It reads JSX text and
string/template literals from the TypeScript AST and skips literals that
are code rather than UI text (imports, types, property names, tagged
templates, values of JSX attributes that are not displayed such as
`className` or `style`, and operands of `===`/`case` comparisons). JSX
text across inline elements and conditional JSX is checked as one
phrase. `--fix` lowercases the reported words. The checker is a
heuristic: it is not meant to model every code shape, so use a
`sentence-case-expect` comment where it guesses wrong.
- Proper nouns (Coder products, role names, third-party products,
protocols, font names) live in `PROPER_NOUNS`. For other deliberate
exceptions, a `sentence-case-expect` comment on the line above
suppresses the report and fails when that line no longer needs it.
- Existing UI text is converted to sentence case, and tests that assert
on it are updated.
- Deployment option lookups (`useDeploymentOptions`) now use CLI flags
instead of display names, so they do not depend on UI wording.
## Performance
`pnpm lint:sentence-case` takes **1.6 s** and is 2% to 4.5% of `pnpm
lint`. Measured on
|
||
|
Dean Sheather
|
d974fefc08 |
chore: sign with github.com/coder/gpgkms instead of scripts/gpgkms (#32308)
Replaces `scripts/gpgkms` with [`github.com/coder/gpgkms`](https://github.com/coder/gpgkms) v0.2.0, the same code extracted into a shared module (terraform-provider-coder already signs its releases with it). v0.2.0 also rejects keys that aren't HSM-backed (`gpg-release` is `HSM`, and the check reads `protectionLevel` from the existing `GetPublicKey` call, so no new IAM is needed), limits each KMS request to a minute, and writes `-out` atomically. - `go.mod`: gpgkms is a `tool` dependency, so the version is pinned in `go.mod`/`go.sum` and Dependabot keeps it current. This bumps go-crypto 1.4.1 → 1.5.2, google.golang.org/api 0.308.0 → 0.311.0 and circl 1.6.3 → 1.6.5, plus a few indirect dependencies. go-crypto is now only indirect: nothing else in coder/coder imports it. - `scripts/gpgkms.sh` (new): runs it with `go tool` (like `scripts/format_go_file.sh` does for gofumpt and gci), passing the release key's OpenPGP identity (name, email, creation time, 4-year lifetime). The library takes these as flags instead of hardcoding them, so they now live in one place. - It also pins `-fingerprint 0F685EFE0AE5A8182A473DD86E3A8E5613707520`, so signing and `public-key` fail if the KMS key or creation time ever change. That's the fingerprint every current main build prints (e.g. run 44031030839), and I recomputed it from the KMS public key and the creation time alone, without signing anything. The fingerprint doesn't cover the user ID or lifetime; the equivalence check below does. - `scripts/sign_with_gpg.sh` and the "Print GPG KMS public key" step in `build.yaml` call the wrapper instead of `./scripts/gpgkms`. Signatures stay armored `.v2.asc` files, as before. - `scripts/gpgkms/` is deleted. ## Same key, same signatures The OpenPGP key's fingerprint depends on these exact inputs, so I checked that nothing changed. With a local RSA-4096 key standing in for KMS, the deleted `newEntity`/`writePublicKey`/`sign` produce the same output as the gpgkms CLI with the flags read out of `scripts/gpgkms.sh`: - The public key is **byte for byte identical**. - A signature with `-prepend` is armored the same way and has the same length (only the timestamp differs). Both the prepended signature and the KMS signature verify in both outputs. - Changing the lifetime in the wrapper by one hour makes the comparison fail, so the check is sensitive. ``` $ git -C gpgkms describe --tags v0.2.0 $ WRAPPER_ARGS_FILE=wrapper-args.txt go test ./cmd/gpgkms -run TestCoderWrapperMatchesOldCoderCode -count=3 -v === RUN TestCoderWrapperMatchesOldCoderCode equiv_coder_test.go:40: wrapper args: ["-name" "Coder Release Signing Key" "-email" "security@coder.com" "-created" "2026-11-16T00:00:00Z" "-lifetime" "35040h"] --- PASS: TestCoderWrapperMatchesOldCoderCode (0.33s) --- PASS: TestCoderWrapperMatchesOldCoderCode (0.11s) --- PASS: TestCoderWrapperMatchesOldCoderCode (0.20s) ok github.com/coder/gpgkms/cmd/gpgkms 0.634s # with -lifetime 35041h equiv_coder_test.go:56: public keys differ: FAIL # with the wrapper's -fingerprint pin and a random test key derived key has fingerprint 9794B34B5E098DE61DD6CE247E0DFD4BF203C917, want 0F685EFE0AE5A8182A473DD86E3A8E5613707520 (wrong -key, -created or KMS key?) ``` (The byte-for-byte comparison runs without `-fingerprint`, since the test key is random.) gpgkms also has its own compatibility test against this identity (`compat_test.go`). Other checks: ``` $ ./scripts/gpgkms.sh public-key # from the repo root (build.yaml) gpgkms: -key is required $ cd scripts && ./gpgkms.sh public-key # from scripts/ (build_go.sh -> execrelative) gpgkms: -key is required $ ./gpgkms.sh sign -key x -prepend ../no-such-file -out o.asc ../go.mod # relative paths resolve from the caller gpgkms: read prepend signature: open ../no-such-file: no such file or directory $ shellcheck -x scripts/gpgkms.sh scripts/sign_with_gpg.sh # clean $ shfmt -d scripts/gpgkms.sh scripts/sign_with_gpg.sh # clean $ actionlint .github/workflows/build.yaml # clean $ go build ./... && go mod tidy -diff # clean ``` Not run here: real signing through Cloud KMS. The first main build after merging prints the public key in the job summary; it should be identical to the one printed by current main builds. --- AI disclosure: this PR was written by an AI coding agent (Xum) at my direction, and the agent ran the verification above. It stays a draft until I've reviewed it. |
||
|
Jake Howell
|
3664834296 |
refactor(site/src/pages/AgentsPage): split out the read-only composer (#32219)
> 🤖 This PR was written by Coder Agents on behalf of Jake Howell. Split the display-only composer out of `AgentChatInput`. `ChatPageInput` now chooses `ReadOnlyChatComposer` explicitly instead of using `readOnlyNotice` as a mode switch, so read-only chats no longer mount the editable composer's hooks or Escape-to-interrupt handler. Reuse the metadata badges, responsive overflow, and mobile menu positioning across both composers. Name the extracted popovers for assistive technology, and cover the split with an Escape regression and dedicated desktop/mobile stories. Closes [CODAGT-1385](https://linear.app/codercom/issue/CODAGT-1385/split-the-read-only-composer-out-of-agentchatinput). Follow-up to #30483. <details> <summary>Implementation decisions</summary> - Keep `AgentChatInput.isReadOnly` for disabled-editor flows; remove only the display-only mode. - Share setup-notice eligibility and active-MCP selection so the two composers cannot drift. - Preserve the existing permission policy, context refresh, queue display, and attachment orchestration. Broader read-only sidebar and permission cleanup stays out of scope. </details> |
||
|
Ethan
|
da0bd0750f |
chore: remove most export_test.go shims (#32162)
Follow-up to https://github.com/coder/coder/pull/25601, where I missed the other way agents avoid `*_internal_test.go`: an `export_test.go` file that re-exports unexported symbols, just so a `package foo_test` test can reach them. There were 13 of these on `main`, most recently from #32063. This PR removes 8 of them. Tests of package internals are now `*_internal_test.go` files, with no changes beyond the package name and the symbols they call. `messagepartbuffer` and `agentcontext` only needed one small accessor each, so `Buffer.EpisodeCount` and `Manager.Started` are just exported for real, and their tests stay where they were. To stop new ones appearing, the `testpackage` linter no longer skips `export_test.go` (the 5 that are left are excluded by path), and `AGENTS.md` and `.claude/docs/TESTING.md` now state the rule. `export_test.go` is an agent idiom, and imo we should try and get rid of it. So, once this PR is approved, we'll fix up all the remaining ones in a follow-up PR, somehow, and undo the lint exclusion when we do. |
||
|
Ethan
|
166b9d25e3 |
test(coderd): remove low-value cron and chatwebhook tests (#32164)
The tests from #32063 and #32062 are two to three times the size of the code they cover, and a lot of them can't fail for a reason we'd care about. This PR removes those, with no production changes. In `coderd/schedule/cron`, two tests rebuilt the schedule rule a second time to compare against, which was also the only use of `export_test.go`, so that goes too. Most of the rest, in both packages, are table rows that take the same branch as a row that stays. I also dropped a copy of the webhook scheme list and a repeated-request test that belongs at the route. What's left is a row per reject branch, the RFC cases, the regression test for the `Next` hang and the constant-time scan. I replayed each fix commit from the two PRs against the smaller suite, and the pre-fix code still fails a test for every one, other than a fix to the wording of a zone error. One row that stays is changed: the bearer wrong-scheme case used `Basic`, which was only rejected because of where its space lands, so nothing covered the scheme word. It's now `Digest`. #32162 overlaps with this in `cron`. With the shim's users gone it no longer needs to touch that package, so it's now stacked on top of this PR. |
||
|
Kyle CarberryandClaude Opus 5.5
|
c0cc6cef4a |
ci: turn off docs PR previews (#32364)
docs-pr-preview-deploy.yaml has failed on every docs PR since 2026-11-17 22:59: its engine job reads the `DOCS_ENGINE_APP_ID` and `DOCS_ENGINE_APP_PRIVATE_KEY` repository secrets, which aren't set. This gates the engine job with `false &&`. The build, deploy and comment jobs need it, so they skip too, and docs PRs show skipped checks instead of failed ones. Previews come back by dropping `false && ` once the job has another way to read docs-engine. `test-docs-preview-mapper.sh` and actionlint pass. 🤖 Generated with [Claude Code](https://claude.com/claude-code) Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com> |
||
|
Jake Howell
|
c1fec5f6db |
feat(site): migrate organization member filters to FilterCombobox (#31786)
> 🤖 This PR was modified by Coder Agents on behalf of Jake Howell. Replace the legacy organization member filter controls with the shared `FilterCombobox`, matching the workspace, template, and audit log filtering UI. - Combine account status and service-account filters in one input with removable chips while retaining URL-backed filter queries. - Preserve free-text searches and advanced query fields when adding or removing filters, and show validation errors on the input. - Reuse shared user status options and add regression tests and Storybook stories for the new controls. <details> <summary>Wording alignment</summary> Use “User type” and “User type is…” to match the deployment Users filter from #29809. Keep the organization-specific “Search and filter members…” placeholder and existing filter behavior. </details> <img width="1100" height="420" alt="image" src="https://github.com/user-attachments/assets/10f66ed9-354f-4196-a4f5-3eb48a0788ae" /> |
||
|
Jake Howell
|
2939dfa7d5 |
feat(site): migrate audit log filters to FilterCombobox (#31783)
> 🤖 This PR was modified by Coder Agents on behalf of Jake Howell.

Replace the legacy audit log filter controls with the shared
`FilterCombobox`, matching the workspace and template filtering UI.

- Combine resource type, action, user, build reason, and organization
filters in one input with removable chips while retaining URL-backed
filter queries.
- List existing audit log presets under a searchable **Show…** section,
and replace existing single-value filters rather than adding conflicting
values.
- Respect user-list and audit-log permissions when suggesting users and
organizations, and update regression tests and Storybook stories for the
new controls.
|
||
|
Kyle CarberryandClaude Opus 5.5
|
555069ef80 |
ci: run eval-coder-agents in its own eval environment (#32363)
The `run` job in `eval-coder-agents.yaml` checks out the PR's head and runs its code, including its own `scripts/harbor-coder`. It currently uses the `main` environment, which holds main-only secrets for other workflows. This moves it to a dedicated `eval` environment, so only eval secrets are ever in scope. - **Depends on** coder/github-org-terraform#124, which creates `eval` (only `main` may deploy, no reviewers, no admin bypass). Merge that first; otherwise GitHub creates `eval` unprotected on the first run. - **`EVAL_CODER_SESSION_TOKEN`:** the job references it, but it isn't set in `main` today. When it's added, put it in `eval`. 🤖 Generated with [Claude Code](https://claude.com/claude-code) Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com> |
||
|
Jake Howell
|
935e0b5735 |
fix(site): migrate template filters to FilterCombobox (#31781)
> 🤖 This PR was modified by Coder Agents on behalf of Jake Howell. Replace the legacy template filter controls with the shared `FilterCombobox` on both the Templates page and AI Settings → Templates, matching the workspace filtering UI. - Combine author, organization, deprecated, and compatibility-mode filters in one input with removable chips while retaining URL-backed filter queries. - Keep `author:me` available to users without permission to list other users, without fetching the user list. - Update the compatibility-mode documentation and Storybook stories for the new controls. <img width="538" height="312" alt="image" src="https://github.com/user-attachments/assets/c7b541eb-0f4e-4456-b31c-70dd85cfe0e9" /> |
||
|
Jake Howell
|
f9c92229cd |
fix: conditionally render <ProxyMessagesList /> (#32210)
Boring fix for conditionally deciding if this is worth rendering a `Errors` and a `Warnings` headings if we have content to actually render inside of them. | Old | New | | --- | --- | | <img width="1139" height="626" alt="image" src="https://github.com/user-attachments/assets/30fa82ab-eb9c-4cc3-bb2b-3c74d6e0c682" /> | <img width="1133" height="515" alt="image" src="https://github.com/user-attachments/assets/ae4f0449-8e92-47ed-8971-1903336e600c" /> | |
||
|
Jake Howell
|
a3e2e8e999 | fix(site): gate template routes and actions by permissions (#31948) | ||
|
Kyle CarberryandClaude Opus 5.5
|
e2abab288b |
ci: mint backport, automation, CI reader, CLA and membership App tokens with Cloud KMS (#32352)
Switches App token steps from `actions/create-github-app-token` with a private key to [coder/github-app-token-action](https://github.com/coder/github-app-token-action). Each App's key becomes a non-exportable Cloud KMS key that only the listed workflow, in its environment, can sign with (coder/gcp#383). | Workflow | App | Environment | Token | |---|---|---|---| | `backport.yaml` | `coder-backporter-app` | `main` | coder: contents, pull_requests, workflows, issues write | | `aigateway-prices-refresh.yaml` | `coder-automations` | `main` | coder: contents, pull_requests write | | `audit-docs-paths.yaml` | `coder-ci-reader` | `main` | coder.com: contents read | | `contrib.yaml` (`cla`) | `coder-cla` | `main` | cla: contents write | | `contrib.yaml` (`community-label`) | `coder-org-membership-bot` | `main` | members read | - **Scope is unchanged:** same repositories and permissions as before. The token is revoked when the job ends. - **Permissions:** each signing job gets `id-token: write`. - **backport.yaml and contrib.yaml community-label:** the old steps set no `repositories`, so the token defaulted to this repository. The action needs it explicitly, so they now say `repositories: coder`; the membership token requests only `members: read`, which is all the App has. - **Tighter than today:** the `main` environment holds all five keys, so any job in `main` could use any of them. Now each key only signs for the one workflow file above, on `main`. - **Secrets:** the KMS key and `APP_KEYS_WORKLOAD_ID_PROVIDER` are already set in the environment. The old private-key secret is deleted after this merges. 🤖 Generated with [Claude Code](https://claude.com/claude-code) Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com> |
||
|
Andrew Aquino
|
ebcf6944dd |
chore(site): drop the @coder/frimousse release age exclusion (#32301)
Removes the `minimumReleaseAgeExclude` entry for `@coder/frimousse@0.4.1` that #32298 added, as discussed in https://github.com/coder/coder/pull/32298#discussion_r4593170186. 0.4.1 was published at 2026-11-16 22:45 UTC. Until 2026-11-17 22:45 UTC, pnpm's minimum release age check fails CI installs (`ERR_PNPM_MINIMUM_RELEASE_AGE_VIOLATION`). Re-run CI after that and merge. 🤖 Generated by Coder Agents on behalf of @aqandrew. |
||
|
|
e0b74e6817 |
docs: add Migrate to Coder section and Microsoft Dev Box migration guide (#31979)
> [!NOTE] > Coder Agents generated this PR. Adds a "Migrate to Coder" group to the docs sidebar with a short index page, and a guide for teams moving from Microsoft Dev Box to Coder. - `docs/install/plan/migrate.md` (new): says who the guides are for and lists them. - `docs/install/plan/migrate/dev-box.md` (new): who it's for, what carries over, a concept-mapping table, 11 numbered migration steps, and **Learn more**. The steps cover the inventory, the control plane, Entra ID (OIDC), templates on Azure (image, network, persistence, access, quotas), customizations and dotfiles, Git auth and secrets, RDP, editors, schedules and hibernation, Intune, and the pilot and cut-over. Each step links to existing Coder docs instead of repeating them. - `docs/install/plan/migrate/ona.md` (moved from `migrate-from-ona.md`): relative links only, plus a redirect from `install/plan/migrate-from-ona` in `docs/redirects.json`. - `docs/manifest/install/plan/migrate.yml` (new) and `docs/manifest/install/plan.yml`: the new group, with the Ona guide under it. This follows the existing `upgrade.md` plus `upgrade/` layout. `docs/manifest.json` is regenerated. Microsoft retirement dates come from Microsoft's own [Dev Box retirement guide](https://learn.microsoft.com/azure/dev-box/dev-box-retirement-guide): the closing-down period started September 14, 2026, and the service retires September 18, 2028. ### Follow-ups outside this PR - **Starter template is broken today.** The registry `azure-windows` template pins `windows-rdp` at `~> 1.0`, which now resolves to 1.4.0. That version requires `agent_name`, so `terraform plan` fails with `agent_name must be set when enable_native_rdp is true.` The copy in `examples/templates/azure-windows/main.tf` also passes `resource_id = null`, which 1.4.0 rejects at `terraform init`. The guide tells readers to set `agent_name = "main"` until both templates are fixed. - **Activity detection docs.** `docs/workspaces/workspace-scheduling.md` and `docs/templates/managing-templates/schedule.md` say only some session types count as activity, but the code counts any connection through the agent (`agent/agent.go` `Collect`, `coderd/workspacestats/reporter.go`). The guide follows the code. Those pages need a separate fix, and an SME should confirm RDP end to end. - **Comparison page.** The coder.com comparison page compares Coder with Windows 365 and VDI, not Dev Box, and still says Dev Box is in "maintenance mode". The guide no longer links to it, so DOCS-1414's comparison-link item waits until the page is corrected. <details> <summary>Reusable outline for future migration guides (DOCS-1414)</summary> The repo has no place for page templates, so the outline lives here. ```md --- title: Migrate from <Platform> to Coder --- <1 to 2 sentences: who it's for (persona and current setup) and the outcome.> <Optional: dated facts about the platform, citing the vendor's own announcement.> ## Before you begin <Access, licenses (mark Premium), cloud permissions.> ## What carries over <Architecture difference in 2 to 3 sentences. "You can keep" list, then "You rebuild" list.> ## Concept mapping | <Platform> (link to the vendor's docs for each concept) | Coder (link to Coder docs) | ## Step 1: Inventory your <Platform> resources ## Step 2: Deploy the Coder control plane ## Step 3: Connect your identity provider ## Step 4: Replace <environment definition> with templates ## Step N: Bring your devcontainer.json (Codespaces, Ona, DevPod) ## Step N: Configure Git authentication and secrets ## Step N: Set up editors (and remote desktops, if relevant) ## Step N: Speed up workspace startup (prebuilt workspaces) ## Step N: Replace schedules and cost controls ## Step N: Move agent workloads ## Step N: Pilot and cut over <One neutral link to the coder.com comparison page, if one exists and is current.> ## Learn more ``` Rules: facts only, with no scoring or positioning language. Check every mapping row against the vendor's current public docs and record the date checked in the PR. Link to Coder docs rather than repeating them. Mark Premium features inline. </details> ### Verified against Microsoft docs checked November 5 and November 10, 2026, in the MicrosoftDocs/azure-docs source (`articles/dev-box/`) and on learn.microsoft.com: - `dev-box-retirement-guide.md` (dates, workload deletion) - `overview-what-is-microsoft-dev-box.md`, `concept-dev-box-architecture.md` (dev centers, projects, pools, definitions, network connections, Microsoft-hosted network, Intune enrollment, Entra join, Windows 10 and 11 client editions) - `how-to-manage-dev-box-pools.md` (local admin or standard user setting) - `concept-what-are-dev-box-customizations.md`, `how-to-configure-team-customizations.md`, `how-to-configure-user-customizations.md` (WinGet, PowerShell, Git-Clone tasks, Key Vault secrets) - `how-to-configure-azure-compute-gallery.md` - `how-to-configure-stop-schedule.md` (one stop time per pool), `how-to-configure-stop-on-disconnect.md`, `how-to-configure-dev-box-hibernation.md`, `how-to-auto-delete-dev-box.md`, `tutorial-dev-box-limits.md` (maximum dev boxes per developer) - `concept-dev-box-role-based-access-control.md`, `how-to-install-dev-box-cli.md`, `how-to-set-up-dev-tunnels.md`, `quickstart-create-dev-box.md`, `how-to-enable-single-sign-on.md` - Intune [supported operating systems](https://learn.microsoft.com/intune/fundamentals/ref-supported-platforms) (Windows client editions, no Windows Server) Coder side: - Registry `azure-windows` template (`main.tf`, `README.md`) and `examples/templates/azure-windows/`: azurerm resources, Windows Server 2022 image, one resource group, virtual network, and storage account per workspace, VM deleted on stop, persistent `F:` disk, `windows-rdp` module, generated admin password shown in metadata, no Entra join, no `daily_cost` - Registry `windows-rdp` module at `release/coder/windows-rdp/v1.4.0`: **Web RDP** (subdomain app) and **RDP Desktop** (Coder Desktop) apps, `agent_name` validation, Devolutions Gateway install from PowerShell Gallery on every start. Reproduced the plan failure with Terraform 1.17.1. - Registry `dotfiles` module: Bash script only - `cli/dotfiles.go`, `cli/dotfiles_windows.go` (`install.ps1`, `bootstrap.ps1`, `setup.ps1`, run with PowerShell, cloned with Git) - `enterprise/coderd/workspacequota.go` (build denied when consumed plus cost exceeds budget), `docs/admin/users/quotas.md` - `coderd/schedule/autostop.go` (autostop requirement stops at the start of quiet hours), `docs/reference/cli/server/index.md` (`CODER_QUIET_HOURS_DEFAULT_SCHEDULE`, `CODER_ALLOW_CUSTOM_QUIET_HOURS`) - `docs/workspaces/workspace-access/remote-desktops.md`, `docs/admin/networking/index.md` (agents must reach the access URL) - `docs/admin/users/oidc-auth/microsoft.md`, `docs/admin/users/idp-sync.md`, `docs/admin/users/organizations.md`, `docs/admin/users/groups-roles.md`, `docs/templates/template-permissions.md` (Premium markers, organization roles) - `coderd/workspacestats/reporter.go`, `coderd/agentapi/stats.go`, `agent/agent.go` (any connection through the agent extends the autostop deadline) - `docs/admin/external-auth.md` (Azure DevOps via Entra ID), `docs/admin/security/secrets.md` - `agent/usershell/usershell_windows.go` (scripts run with PowerShell on Windows) - No hibernation feature exists in the Coder codebase. Checks run: `make gen/docs-manifest`, `make pre-commit-light` (markdownlint, `lint/emdash`, `lint/docs-redirects`, typos), Vale (0 alerts on the new pages), `lint/docs-html`, `lint/docs-manifest`, `docsredirectscheck -base origin/main -branch main`, a check that all 159 relative links and anchors in the three pages resolve, and a `doc-check` self-review. ### Open questions for the reviewer - **Intune and Entra join:** the guide says Coder doesn't enroll workspaces in Intune, that Intune needs a Windows client image, and links Microsoft's Entra VM sign-in docs. Should a separate guide cover setting up Intune with Coder? - **Windows client editions:** the guide tells readers to check Microsoft licensing before using Windows 10 or 11 images on Azure VMs. It makes no licensing claim itself. - **Windows support in registry modules:** the guide now says the `dotfiles` module is Bash only. Whether `git-clone` and other modules work on Windows is unverified. Closes DOCS-1414, Closes DOCS-1416 Supersedes #31807, reopened under a human author for attribution. --------- Co-authored-by: Coder Prototypes <294797144+coder-prototypes@users.noreply.github.com> Co-authored-by: Ian Evans <5760366+ianjevans@users.noreply.github.com> |
||
|
Kyle CarberryandClaude Opus 5.5
|
85a786c4fa |
ci: mint release and package publisher App tokens with Cloud KMS (#32331)
Switches every GitHub App token step in the release workflows from `actions/create-github-app-token` with a private key to [coder/github-app-token-action](https://github.com/coder/github-app-token-action). Each App's key becomes a non-exportable Cloud KMS key that only these workflows, in their environments, can sign with. **`coder-release-publisher`** - `release.yaml` (environment `release`): the tagging token and the release-publishing token. - `create-release-branch.yaml` (environment `release-refs`, `main` only): the release-branch token. The job gets `id-token: write`. - Scope is unchanged: `repositories: coder`, `contents: write`, `workflows: write`. **`coder-package-publisher`** - `release.yaml` `publish-packages` (environment `release-publish`): `repositories: packages`, `contents: write`. - `release.yaml` `publish-homebrew` (environment `release-publish`): `repositories: homebrew-coder`, `contents: write`, `pull_requests: write`. - Both jobs get job-level `contents: read` and `id-token: write`. Before, they inherited the workflow's `contents: read`. **Unchanged** - Who approves: every environment still needs a release manager, and admins can't bypass. - Each token covers one repository and is revoked when its job ends. - The KMS keys, `APP_KEYS_WORKLOAD_ID_PROVIDER` and the App IDs are environment secrets, already set in `release`, `release-refs` and `release-publish`. Release branches 2.39, 2.38, 2.37, 2.34 and 2.29 run their own `release.yaml` and get the same change once this merges. The old private keys are deleted after that. 🤖 Generated with [Claude Code](https://claude.com/claude-code) --------- Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com> |
||
|
Jon Ayers
|
9c79ab71bb | ci: stop rcodesign finalizing and unloading the PKCS#11 module (#32333) | ||
|
Ben Potter
|
ed9e9a84ec |
docs: add sandbox agents guide and startup time tips (#32280)
Adds a "Sandbox agents" guide under Extending templates, and adds startup time tips from the [Improving Coder Workspace Startup Times](https://www.youtube.com/watch?v=-xcVJQWVCxs) livestream to the speed-up templates guide. **Sandbox agents** (`docs/templates/extending-templates/sandbox-agents.md`) is organized around three traits: kernel, network, and secrets isolation, plus fast startup. Each trait has a short methods table with tradeoffs, plus examples and references. - Starts with the coder-labs registry templates (agent-sandbox, Plain Sandbox, OpenShell) that implement all three, and calls out [agent-sandbox](https://agent-sandbox.sigs.k8s.io/). - Explains what the sandbox covers for CLI Agents, Coder Agents, and Agent Relay. - Shows how to define sandbox profiles as immutable parameters with one preset each, and how to control which profile an agent gets. - Kernel: gVisor, Kata, and EKS Nitro Sandboxes (`isolated-sandbox` RuntimeClass in EKS Auto Mode). - Network: separate proxy Pod vs. sidecar, example rules using an internal GitHub and artifact store, and a cloud firewall layer (AWS Network Firewall, Route 53 Resolver DNS Firewall) that also limits DNS. - Secrets: `api_key_scope = "no_user_data"`, a scoped AI Gateway token (skipped for prebuilds, optional `lifetime`), per-workspace EKS Pod Identity, and just-in-time credentials from Vault. **Speed up templates** (`docs/workspaces/speed-up-templates.md`) gets new sections for pre-warming Kubernetes nodes (with GKE, EKS, and AKS alternatives), building tools into the image, prebuilt workspaces (including one preset for each configuration), and skipping the Kubernetes rollout wait (with coder-logstream-kube to surface Pods that can't start). It links the [fast-workspaces-lab](https://github.com/coder-contrib/fast-workspaces-lab) repo for the sample base image, node schedule, and prebuild templates. **Agent Firewall** gets a notice on its index page and in the glossary that it is being phased out, pointing to the sandbox guide. The sandbox guide doesn't mention Agent Firewall. Two diagrams in the speed-up templates guide come from the talk's slide deck, cropped to the diagram. Notes for reviewers: - The scoped AI Gateway token (`user:read_personal`) isn't tied to a workspace, so with several organizations, AI Gateway uses the user's effective group for budgets. The page doesn't mention this. - The Nitro (coder/registry#1253) and Cilium (coder/registry#1254) registry templates are still open, so they aren't linked yet. <details> <summary>Decisions and checks</summary> - **Structure:** three traits, several ways to get each, and simple tradeoffs. - **Sysbox** is not listed as kernel isolation, because system calls still reach the node's kernel. - **Deployments** stay the recommendation over bare Pods, because `wait_for_rollout` and coder-logstream-kube cover the startup and error cases. - **Token lifetime** is left commented out in the example: Coder can't revoke the token at stop, and a lifetime shorter than autostop breaks running workspaces. - **Process logging** wording: the eBPF sidecar runs inside the sandbox with gVisor, Kata, or Nitro, so the page asks readers to test it. - **"CLI Agents"** is kept as the term for agents that run fully in the workspace. - **Verified in code:** - `mutable = false` is enforced on later builds (`coderd/dynamicparameters/resolver.go`). - Presets match by subset, also without a `preset_id` (`coderd/database/queries/prebuilds.sql`, `coderd/workspaces.go`). - `no_user_data` blocks the Git SSH key and external auth (`coderd/gitsshkey_test.go`, `coderd/externalauth_test.go`). - Token creation is rejected for the prebuilds system user (`coderd/apikey.go`), and the default token lifetime is 7 days (`codersdk/deployment.go`). - No Coder code sets `CODER_SESSION_TOKEN` in a workspace; registry modules such as `coder-login` do. - **Checks run:** `make lint/emdash`, `make lint/docs-html`, `make lint/docs-manifest`, markdownlint, markdown-table-formatter, Vale (0 errors), and the pre-commit hook. </details> 🤖 This PR was generated by Coder Agents on behalf of @bpmct. |
||
|
Nick Vigilanteandcoder[bot]
|
da64286fe3 |
docs: fix GerundHeading, Semicolons, and UnitSpacing findings (#31990)
Fixes the `warning`-level findings that the Vale findings spike review marked valid: - **`Coder.GerundHeading`**: `docs/.style/styles/Coder/README.md`, "Authoring a new rule" is now "Author a new rule". Nothing links to the old anchor. - **`Coder.Semicolons`**: `templates/extending-templates/docker-in-workspaces.md`. Each semicolon is now a sentence break, with the new sentence on its own line. - **`Coder.UnitSpacing`**: added ` ` between number and unit in `get-started/index.md` (10 minutes), `mcp-server.md` (5 minutes), `ai-governance/ai-gateway/setup.md` (60 days), and `reference/feature-stages.md` (60 seconds). These three rules now have 0 findings in `vale docs/`, and the changed files have no new findings from other rules. --- AI-generated by Superblink on behalf of @nickvigilante. Supersedes #31877, reopened under a human author for attribution. Co-authored-by: coder[bot] <137810501+coder[bot]@users.noreply.github.com> |
||
|
Paweł Banaszewski
|
a3f25a491e |
feat: forward bridged routes in AI Gateway proxy mode (#30226)
Enable bridged request forwarding in AI Gateway proxy mode. Responses are captured through `TeeBuffer`. Proxies are created per-request reusing transports. Handle `http.ErrAbortHandler` inside the circuit-breaker wrapper so aborted responses are classified by HTTP status before the panic is propagated. Generated by Coder Agents on behalf of @pawbana. |
||
|
Mathias Fredriksson
|
fe0b6e5de0 |
fix: take chat state from the stream only (#30478)
The chat page got a chat's messages, queue and status from three places: REST pages, action responses and stream events. None of them had a version, so the client could not tell which was newer and reconciled them with rules of its own. A refetch or a response could replace newer state from the stream, and a stream message that failed to parse lost its events and left an error until a reload. The server now returns snapshot_version on the newest messages page and on stream events (#29662), which makes one copy enough. Each chat has a store that loads the newest page once; after that, only stream events and older pages change it. To reconnect, to return to a chat within five minutes, or to recover from a failed parse, the client opens the stream again at the highest version it applied. It refetches no messages, so no response replaces what the stream set. The client no longer reads messages or queue rows from action responses, so a send, an edit or a queue change would show only once the stream reports it. The store therefore shows the action's direct effect at the click and keeps it until the stored state holds the result or the request fails. It does not end at the next stream event of a kind, because that event can report another change, and the user's change would disappear and come back. A sent message has no ID until the server creates it, so pending sends are matched to new messages in click order, and a chat's send, edit and queue requests run one at a time to keep that order. This assumes one user in one client. A message from an agent, an automation or another API client can end a pending send early, and the next stream event corrects it. The composer clears at the click, because the chat already shows the sent message. It stays editable, so text typed during the request is kept. Closes CODAGT-903 |
||
|
Mathias Fredriksson
|
99e3bf91a7 |
fix(coderd/database/migrations): resolve duplicate version (#32329)
Main cannot initialize database migrations because #32309 reused version 000643, already taken by the skill display-name migration from #31747. Renumber the later chat-project migration and its fixture to 000644, preserving the earlier migration number. All three renames leave SQL contents unchanged. |
||
|
christin
|
7d98748885 |
fix(site/src/pages/WorkspacesPage): meet 24px target size for the workspace sharing indicator (#32321)
The "Workspace permissions" trigger (people icon next to the owner name in the workspaces table) was a 14×16px button with the workspace name link directly above it, so it failed WCAG 2.5.8 (axe `target-size`) on both size and spacing. The trigger is now 24×24px. The extra area extends sideways and downward only, and negative margins cancel it out, so the icon stays in the same place and the row height does not change. If the target grew upward too, it would cover the bottom of the workspace name link, and axe would then flag that link as partially obscured. A new `TriggerFocused` story tabs to the trigger, so Pixel captures the 24px focus ring. Closes DEQ-361 | Ticket | UI surface | Screenshots | |---|---|---| | DEQ-361 | `/workspaces` table, sharing indicator next to the owner name | [Linear comment](https://linear.app/codercom/issue/DEQ-361/target-does-not-meet-minimum-size-or-spacing#comment-5ba3bb9c) | **Verification** - On the dev server at `/workspaces` with one shared workspace, axe-core 4.11 `target-size`: - before: one violation on the trigger (`14px by 16px ... safe clickable space 16px`); - after: no violations. The trigger is 24×24, the icon sits at the same x/y as on `main`, and the row is still 72px tall. - `pnpm check`, `pnpm lint` (including `tsc`), and the story tests for `WorkspaceSharingIndicator.stories.tsx` pass. - The existing hover stories render the trigger in a plain block rather than a flex row, so the -8px bottom margin may cause small Pixel diffs there. <details> <summary>Decision log</summary> - Batch label `target-size-small` contains one eligible ticket, DEQ-361, so this is one root cause and one PR. - I fixed the call site rather than `TooltipTrigger`. The shared interactive trigger wraps content of many sizes, and other callers already size it themselves. - First attempt: `size-6 -m-1.25` (symmetric). It fixed the trigger, but on the real page axe then flagged the workspace name link as partially obscured. I switched to `-mx-1.25 -mb-2 pb-2`, which grows the target only into the empty cell padding below. - Tradeoff: the focus ring now has 1px above the icon and 9px below it, so it is not centered. The ticket has `ux-input-needed`, so design may want to weigh in. - Test: I wrote a play-function geometry assertion and confirmed it failed on `main` (14 < 24) and passed on the branch. I then dropped it, because FE1 and FE10 prohibit geometry assertions in play functions. Story-only coverage follows the precedent in #30844. - Self-review: `frontend-review` found no FAILs. `frontend-deep-review` found no blocking or should-fix issues; I fixed its nits (the comment wording and a redundant `self-start`). `frontend-accessibility` passes `target-size`, `button-name`, `nested-interactive`, and `aria-allowed-attr`. </details> 🤖 Generated by Coder Agents on behalf of @chrifro. |
||
|
Susana Ferreira
|
3211ca066e |
feat: add organization unpriced AI models endpoint (#31753)
## Description

Adds the experimental `GET
/api/experimental/organizations/{organization}/ai/model-prices/unpriced`
endpoint behind the "N models not set up" warning on the organization AI
spend page
([Figma](https://www.figma.com/design/6TkixpkUIM5Qv6I7qhM3xZ/AI-Gov---user-spend?node-id=70-11964&t=KQwENGjcQvVT9qkh-4)).
It lists the models used in the period that still hold no price in the
organization, using the query from this stack.

## Changes

- Add the `organizationUnpricedAIModels` handler and
`ExperimentalClient.OrganizationUnpricedAIModels`:
- Reuses `aiSpendRetainedPeriod`, since token usage is subject to data
retention.
- Returns the applied period, `count`, and `models` (provider name,
display name, icon and type, model, token count), most unpriced tokens
first.
- Requires read on the organization's model prices (owners and
organization admins), so the UI only requests it for users who can set
prices.
- Add handler tests for the response, period validation, organization
scoping and role access.

Note: pagination will be added in a follow-up.

Closes AIGOV-730

> [!NOTE]
> Generated by Coder Agents on behalf of @ssncferreira.
|
||
|
Jaayden Halko
|
1f1aa6ae3c |
feat: add chat project template schema and queries (#32309)
Adds the database layer for attaching workspace templates to chat projects: the schema, the queries, their authorization, and the audit type. Nothing calls the new queries yet, and the existing create and update handlers pass the new parameters unset. The API, the limit's enforcement, and the agent tools follow in the PRs above. - Attachments live in a `chat_project_templates` table (`project_id`, `template_id`, `created_by`, `created_at`), deleted with the project or the template. `chat_projects` gains `limit_templates` (default `false`), `default_template_id`, `default_template_version_preset_id`, and `default_parameters jsonb`. A project stores a default preset or default parameter values, not both. - `InsertChatProjectTemplates` needs project `update` and `use` on every template. It skips templates that are already attached, and templates outside the project's organization, so an attachment never crosses organizations. `DeleteChatProjectTemplate` needs project `update` and template `read`, and clears the project's default when it detaches the default template. Both checks are in dbauthz. - `GetChatProjectTemplatesByProjectIDs` is authorized through the project, and leaves out deleted, deprecated, and agent-disabled templates. It does not check the caller's access to each template, so callers do that before they expose one. - `UpdateChatProjectByID` changes the template settings only when the request sets them, so an update that omits them cannot write back a stale snapshot. - `AuditableChatProjectTemplates` is the audit form of a project's attached templates, logged as a write to the project. The new `chat_projects` columns are tracked in the project's own audit diff, with the default parameter values masked because they may hold credentials. **NOTE**: the migration adds one table and four columns and changes no existing rows. Existing projects keep unlimited template access. Stack (merge top to bottom): - #32309 👈 - #30754 - #32310 - #30755 - #30756 - #30898 |
||
|
Garrett Delfosse
|
7394a66e72 |
test(codersdk/toolsdk): fix TestTools/WorkspaceExecute workdir check on Windows (#32323)
Fixes CODAGT-1333. `TestTools/WorkspaceExecute` failed on Windows with `GetFileAttributesEx /tmp: The system cannot find the file specified.` The agent runs commands via `sh -c` on every platform (`agent/agentproc/process.go`), which is Git Bash/MSYS on Windows runners. There `pwd` prints a POSIX path like `/tmp/...`, and `filepath.EvalSymlinks` cannot resolve it. The command itself ran in the right directory; the assertion was wrong. The test now runs `touch marker.txt` in the requested workdir and asserts the file exists at `filepath.Join(workDir, "marker.txt")` on the host. This is the same approach `agent/agentproc` `CustomWorkDir` already uses for this reason. No timeouts changed. --- _Generated by Coder Agents on behalf of @f0ssel._ |
||
|
Spike Curtis
|
707083166a |
test(cli): fix flake due to UDP crosstalk (#32102)
fixes ENT-252 In a port forward test for UDP, there are actually 2 UDP socket on the remote side (the local side uses a mocked network). There is the target socket where our echo server is listening, and the UDP socket that the workspace agent opens up to talk to it. We must be getting crosstalk on the workspace agent socket, because the echo server was already filtering based on prefix. The solution in this PR is to move the filtering all the way back to the test function itself, so if crosstalk comes either on the echo socket or the workspace agent socket, we'll forward it across the tailnet, but ultimately filter it in the test function before asserting. --------- Signed-off-by: Spike Curtis <spike@spikecurtis.com> |
||
|
Molly Fraser
|
e9c4fb142f | test(enterprise/cli): use quartz clock in standalone AI Gateway shutdown tests (#32095) | ||
|
Jake Howell
|
8d547034c0 |
fix: resolve dropdown menu background and alignment (#31883)
> 🤖 This PR was modified by Coder Agents on behalf of Jake Howell. Better aligns the submenu items with their content. Furthermore, highlights the parent item that opened the submenu. | Old | New | | --- | --- | | <img width="790" height="471" alt="Image" src="https://github.com/user-attachments/assets/9a32777a-8dcc-4b27-8414-e449e844c984" /> | <img width="816" height="471" alt="Image" src="https://github.com/user-attachments/assets/27094d23-ac37-4fbc-92c1-3573bf7916a1" /> | |
||
|
Roo Thorp
|
0b5083440f |
fix(aibridge): correlate Responses API tool results followed by developer messages (#32053)
When a user approves a command with "Yes, and don't ask again", a developer message is appended after the tool result. `correlatingToolCallID` only checked the last `input` item, so these requests weren't correlated and the session page split the agentic loop into a new thread with no prompt. `correlatingToolCallID` now walks back from the end of `input`, and skips developer/system messages and reasoning items. The request is correlated if the first remaining item is a tool result with a `call_id`. A user message or any other item means a new turn, so it isn't correlated. Fixes AIGOV-727 Generated by Coder Agents on behalf of @roothorp |
||
|
Mathias Fredriksson
|
c3ff770e8a |
fix(coderd/database): match workspace requester by owner ID when sorting (#32188)
GetWorkspaces sorted the requester's favorite and own workspaces first by matching the owner's username. Usernames are unique only among non-deleted users, and a deleted user keeps theirs, so a user who took a deleted user's username saw that user's deleted workspaces and favorites sorted as their own when listing deleted workspaces. Match by owner_id instead, as the sort did before #22290. The username form most likely worked around the sqlc CTE bug: with the EXISTS (tasks) filter the query had then, sqlc without the coder/sqlc fix rejected the bare owner_id as ambiguous. #29085 removed that filter, so the owner_id form generates with either sqlc. |
||
|
Jaayden Halko
|
4866d0fb1f |
feat: add display names to project skill actions (#31747)
closes CODAGT-1506 Project skill action chips show the skill's slug (`deploy-bot`, `security-review`), because skill names must be kebab-case. This adds an optional display name that labels the chip instead. Project skills get a `display_name` column, set through `display_name` on the create and update requests. It is limited to project skills (the same rule as `action`), trimmed, single line, and at most 64 Unicode code points. The chip, its tooltip, and the "More" menu show the display name, sort by it, and fall back to the skill name when it is empty. When a display name is set, the tooltip and the menu item also show the `/name` slash command, so actions that share a display name stay distinguishable. Clicking an action still inserts `/name`, and the `/` menu is unchanged. The project skill editor shows a **Display name** field under **Show as action** only while that switch is on. Turning the switch off hides the field but keeps its value, and saves omit `display_name` while the action is off, so the stored value stays. The display name lives in the database rather than SKILL.md frontmatter, so downloading and re-importing a skill does not carry it. To share the code-point length check with the editor, `countCharacters` and `maxCharacters` move from `ChatProjectDialog.tsx` into `site/src/utils/formUtils.ts`. <img width="637" alt="Project skill editor with the Display name field under Show as action" src="https://raw.githubusercontent.com/coder/coder/assets/pr-skill-action-display-name/pr/edit.png" /> <img width="520" alt="Action chips labeled with display names, with the tooltip open" src="https://raw.githubusercontent.com/coder/coder/assets/pr-skill-action-display-name/pr/chips.png" /> Refs CODAGT-1506 |
||
|
Mathias Fredriksson
|
d3e471feb0 |
fix: bump sqlc fork to restore CTE scope tracking (#32187)
Without coder/sqlc's CTE scope fix (coder/sqlc#1), sqlc rejects valid queries that put a subquery inside a CTE with a false "column reference is ambiguous" error. The fix only ever existed on the side branch the old pin pointed at. #25105 moved the pin to the fork's merge of upstream v1.31.1, which didn't include it, so the fix was silently dropped. No current query hits the bug, but the next one would have failed at make gen. The fix is now on the fork's main. Generated code is unchanged. |
||
|
Ehab Younes
|
d611c80330 |
feat(agent): detect Zed SSH sessions (#32258)
Zed connects over plain SSH and sends no app name, so its sessions show up as SSH. When no app name is set, the agent now labels a session `zed` if its command starts Zed's remote server proxy (`zed-remote-server-… proxy --identifier …`). `zed` was already in the list of apps Coder knows, so it now shows up in session counts, connection logs and metrics with no server change. Closes ENG-359 |
||
|
Jake Howell
|
61ea77f8f6 |
feat(site): warn when workspace logs are truncated in Agents chat (#32305)
> 🤖 This PR was modified by Coder Agents on behalf of Jake Howell. Agents chat now warns when workspace build or agent startup logs reach the storage limit. Startup warnings include `/tmp/coder-startup-script.log` as a recovery path. Keep known truncation warnings visible when logs are empty or fail to load. Preserve overflow-only workspace updates, recover completed-build metadata after workspace lookup failures, and retain historical build metadata when a newer build starts. Show a separate notice when truncation status cannot be checked. Refs CODAGT-1185. <details> <summary>Validation and review decisions</summary> - Passed 24 focused unit tests and 14 Storybook tests, `pnpm check`, `pnpm lint`, `pnpm format:check`, `make lint/emdash`, and `git diff --check`. - Regression tests cover overflow-only build and agent updates, the build-ID fallback after workspace lookup failure, and metadata retention across a newer-build watch event. Stories cover empty, waiting, and failed log output. - Checked the five added Storybook states in dark and light themes at desktop and 320px widths. Axe reported no violations or incomplete results; keyboard focus checks passed. No actual screen-reader test or base-branch visual comparison was run. - Completed the frontend pattern check, eight independent frontend review roles, test audit, and documentation self-check with no remaining blocking or should-fix findings. No product-docs changes were needed. - Reused the existing React Query cache for historical metadata rather than adding polling or mirrored state. Story query fixtures are local to each story, and exported query-key helpers are documented. - Corrected the earlier accessibility assessment: tool output already renders inside the transcript's `role="log"` live-region ancestor. No nested live region was added. The Codex accessibility thread remains open because actual screen-reader announcements have not been verified. </details> <img width="631" height="213" alt="image" src="https://github.com/user-attachments/assets/f77f89fd-3a3a-4650-b9c7-abf33faba62f" /> |
||
|
Jake Howell
|
f1c5983695 |
fix(site): persist workspace upload drafts (#32221)
> 🤖 This PR was modified by Coder Agents on behalf of Jake Howell. Completed but unsent workspace-upload chips disappeared when leaving a chat or when an optimistic workspace rebind rolled back, even though the files remained in the workspace. Persist compose-draft metadata by chat and workspace, restore completed references when returning, and clear them on successful send or explicit removal. PNGs use the normal image-attachment path, which already persists drafts, so they do not reproduce this issue. To reproduce the original bug, upload a `.zip` or `.tar` in an existing chat with a running workspace, wait for completion, **do not send the message**, then switch chats and return. Check whether the unsent composer chip survives, not whether the file remains in the workspace. Refs [CODAGT-1172](https://linear.app/codercom/issue/CODAGT-1172) and #27080. <details> <summary>Implementation decisions</summary> - Store metadata only in browser localStorage. File bytes stay in the workspace; there is no backend change or cross-device synchronization. - Enable persistence only for the existing-chat composer, keeping message edits and deferred new-chat uploads separate. - Preserve previous scopes for navigation and rebind rollback, cancel unfinished uploads, and ignore stale worker completions. - Warn on storage failures without blocking the current draft. Keep previously saved references when they are still current; otherwise attempt to clear stale metadata so removed files do not return. </details> |
||
|
Sas Swart
|
4ac8f0a2aa |
docs: document how AI Gateway assigns a request's organization (#31925)
Documents how AI Gateway assigns every request to one organization, and how that organization now decides the effective group, budget, overrides, and spend. Adds a **Request organization** page and corrects pages that still described budget resolution as deployment-wide. Refs AIGOV-753. Describes behavior merged in #30902, #31118, #31119, #31120, #31121, #31583, and #31584. ## Changes - New page `docs/ai-governance/ai-gateway/request-organization.md` (sidebar, after Cost control): resolution order, the effective group fallback, rejected requests, what the organization controls, a multi-org worked example, reports that still resolve across all orgs, and the caveat for standalone gateways older than v2.40. - `cost-controls.md`: removes "the effective group is deployment-wide", scopes overrides and effective group resolution to the request's organization, and adds the reporting caveat. - `standalone.md`: older replicas check budgets across all organizations. - `coder-agents/platform-controls/{index,spend-management}.md`: these said an override beats every group budget, which is no longer true for chats in another organization. ## For reviewers - **Mismatch rejection is not documented.** The ticket and RFC describe rejecting a workspace/chat org mismatch. A chat can only bind a workspace in its own org (`coderd/exp_chats.go`), chatd requests resolve to the chat's org even with a workspace, and no client request can carry both inputs. The page says the two always agree instead. - **"v2.40" is inferred.** `release/2.39` is on aibridged API v1.5 and `main` is on v1.6, so v1.6 ships in v2.40. A 2.39.x backport would make this wrong. - **Custom prices.** The price lookup reads per-org prices, but no API or CLI can set them yet, so the page says custom prices apply in every org. This needs an update when per-org prices ship. - **Site-wide reports.** The avatar menu, Agents usage indicator, `GET /api/v2/users/{user}/ai/spend`, Members tab budget, Groups page combined limit, and `blocked_users` metric still resolve across all orgs (`TODO(AIGOV-527)`), so they can disagree with what was enforced. ## Release note draft ```markdown - AI Gateway budgets and spend follow the request's organization (#31119, #31120, #31121, #31583, #31584) > Every AI Gateway request now belongs to one organization: the workspace's organization for workspace session tokens, the chat's organization for Coder Agents, and otherwise the organization of the user's effective group. Budgets, user overrides, and spend apply within that organization only, instead of across all of the user's organizations. Users in one organization see no change. Users in several organizations can hit a smaller budget, or have no limit at all, in another organization's workspaces and chats. Requests are rejected when the user is no longer a member of the workspace's or chat's organization, or of any organization. > > Migration: Set budgets in every organization your users send AI requests from. Upgrade standalone AI Gateway replicas to v2.40. Older replicas keep checking budgets across all organizations until upgraded. ``` ## Validation `make pre-commit-light`, Vale on the changed files, and `make lint/docs-manifest` pass. A `doc-check` author self-check found 13 blocking findings, all fixed. Not applied: a suggested test pinning the site-wide spend endpoint (code change, out of scope for this docs PR). <details> <summary>Decision log and verified behavior</summary> Sources: AIGOV-753, epic AIGOV-749 and its delivered tickets (AIGOV-712 to 716), the canceled AIGOV-717, and the RFC "AI Gateway Model RBAC and Org-Scoping" (Phase 1). Verified against `main` (`a3aab79775`): | Claim | Evidence | |---|---| | Order: workspace session token, chat org, site-wide effective group | `coderd/aibridgedserver/orgresolver.go` `resolveOrganization` | | Workspace session token = `coder_workspace_owner.session_token` | `provisionerdserver.WorkspaceSessionTokenName`, `workspaceAttribution` (API tokens excluded) | | Rejections return `403 unauthorized` | `coderd/aibridged/http.go` IsAuthorized failure path | | Rejected: deleted workspace, not a member of the workspace/chat org or org deleted, no live org | `orgresolver.go` `ErrUnknownWorkspace`, `ErrUnknownOrganizationMember`, `ErrNoOrganization` | | Chat request takes chat org even with a workspace | `enterprise/aibridged_integration_test.go` "delegated organization with workspace" | | With an org, only that org's groups, override, and Everyone group count | `coderd/aibridge/budget/budget.go`, #31119 | | Fallback with no budgets: default org, then earliest membership | `GetUserEveryoneFallbackGroup` | | Budget counts only spend recorded against its group | `GetUserAISpendSince` keyed on `effective_group_id` | | Notifications use the per-request effective group | `coderd/aibridgedserver/notifications.go` | | Per-org prices not settable | `UpsertOrganizationAIProviderModelConfig` has no non-test caller | | v2.39 gateways: site-wide budget check, no org recorded | `release/2.39` `coderd/aibridged/http.go`, `aibridge/recorder/drpc_recorder.go` | Page vs. section: a dedicated explanation page, because `cost-controls.md` is already long and RFC Phases 3 and 4 (model RBAC, "require organization scope") will build on the same resolution rules. </details> --- *This PR was generated by Coder Agents on behalf of @SasSwart.* |
||
|
Thomas KosiewskiandJaayden Halko
|
47c1357cce |
feat(site/src/pages/AgentsPage): share the attachments request and Git view helpers with the overview card (#31411)
Moves two pieces of shared logic out of their single owners, so the overview card container in #31590 can read them without copies, and lets the card view show a failed attachments request. The Git panel behaves as before. The Summary panel behaves as before except for its failed attachments request, which now shows the same one-line alert as the card. 1. `hooks/useChatAttachments.ts` takes the Summary panel's attachment list: the files in the loaded messages, then the server's `chatAttachments` list for the messages before them. It also owns the request state and the retry (`earlierAttachmentsRequest`). The card and the panel read the same React Query key, so the earlier-attachments request runs once. 2. `components/GitPanel/gitViews.ts` is a pure module for `GitView`, `viewIdFor`, `DiffStats`, `computeRepoStats`, `repoLabel`, and `repoBranchLabel`. `GitPanel` imports them, and `RepoHeader` uses `repoBranchLabel` instead of its inline branch label. The card view types its repository rows with `DiffStats`. 3. The card view takes `earlierAttachmentsRequest`. When the request fails, Attachments shows the error and a **Retry** button. The section shows even when no attachment loaded, and the card no longer says "Nothing to show yet" then. 4. The new `AttachmentsErrorAlert` renders that error in both the card and the Summary panel. The full `ErrorAlert` was too tall for both: the server message wrapped, and the panel pushed **Retry** below its fold. The new alert is one row with a fixed "Failed to get attachments" message, no debug detail, and an extra-small **Retry** button. | Overview card | Summary panel | |---|---| | 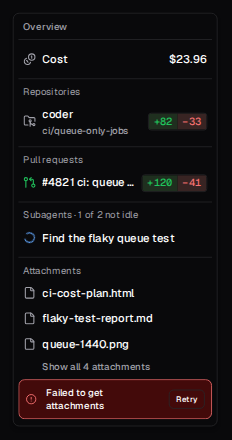 | 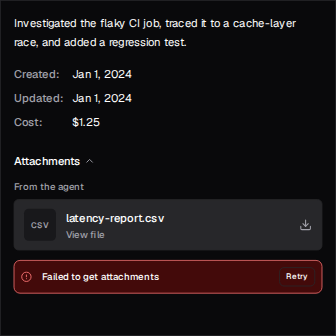 | ## How to test 1. Run `pnpm test src/pages/AgentsPage/components/ChatSummaryPanel.test.tsx src/pages/AgentsPage/components/ChatOverviewCardView.test.tsx src/pages/AgentsPage/components/GitPanel/GitPanel.test.tsx` in `site/`. 2. In Storybook, open `GitPanel`. Nothing changes visually. Open `ChatSummaryPanel`. Only the `EarlierAttachments*` stories with a failed request change, to the one-line alert. 3. Open `ChatOverviewCardView`, story `EarlierAttachmentsError`, and `AttachmentsErrorAlert` for the new alert at the card width (idle and retrying) and the list width. ## What to look at first 1. The retry state in `useChatAttachments`. A retry clears the error of a query with no data, so the hook keeps the failed error until the retry settles. The test "keeps the failure and its retry button while the retry runs" fails without this. 2. `AttachmentsErrorAlert` lays the message and **Retry** on one row with child selectors (`[&>div>div]`, `[&>div>div>div]`) on `Alert`'s internal markup. A change to `Alert`'s nesting would undo the layout, which the `AttachmentsErrorAlert` stories would catch. The alert also no longer shows the server's error message. 3. `computeRepoStats` in `gitViews.ts` drops the `if (!repo.unified_diff) continue` branch. An empty diff counts zero lines and stays out of the map, so the result is the same. <details> <summary>Review history</summary> Follow-up fix: the card view shows a failed earlier attachments request with a retry. `useChatAttachments` exports its `EarlierAttachmentsRequest` type for the view, and `OverviewListSection` takes `children` after its rows. A new test clicks **Retry** and checks the callback. It fails when the section drops its `children`. The PR title changed from `refactor` to `feat` for this. Polish pass changes: added `gitViews.ts` and the retry test. The PR title changed from "move the chat attachments list into a hook" to cover the Git helpers. Final round fixes: renamed the hook's `earlier` result to `earlierAttachmentsRequest`, typed the card's repository rows with `DiffStats`, and made the retry test assert the visible error and wait for the retry to finish. Declined in the final round: - Keep `computeRepoStats` private in `GitPanel.tsx`. The requester asked for it in `gitViews.ts` next to the other Git view helpers. - Delete the retry test because the `EarlierAttachmentsRetrying` story covers the state. The requester asked for this test. It fails in CI when the alert disappears during the retry, while the story only changes a screenshot. - Pass `earlierAttachmentsRequest` to `ChatAttachments` as one prop. It saves about six lines but touches the `ChatAttachments` stories. Smaller error alert: added `AttachmentsErrorAlert` and used it in the card and in `ChatAttachments`. The `EarlierAttachmentsFailed` story no longer scrolls **Retry** into view, since the alert fits the panel. The retry test no longer checks the server's error text, which the alert stopped showing. It still checks that **Retry** stays disabled during the retry and disappears after it. </details> --- _Generated with [`xum`](https://github.com/coder/xum) • Model: `anthropic:claude-opus-5-5` • Thinking: `high`_ --------- Co-authored-by: Jaayden Halko <jaayden.halko@gmail.com> |
||
|
Jake Howell
|
54d9888bb6 |
fix: restore border to prerelease version badge (#32307)
This got destroyed during removing unnecessary border classes 🥲 Just moving it back to the right spot with corrector CSS. | Old | New | | --- | --- | | <img width="217" height="41" alt="image" src="https://github.com/user-attachments/assets/9de053dd-8723-48e1-8136-9e1b3d1c9849" /> | <img width="197" height="35" alt="image" src="https://github.com/user-attachments/assets/f64ee3c9-c670-4565-b97d-de960c3b1605" /> | |
||
|
Jon Ayers
|
e853deecb4 | ci: pin the Rust toolchain that builds rcodesign (#32306) | ||
|
Jay
|
2697760519 |
fix(site): prevent template Source Code tab from overflowing the page (#32173)
Fixes #32172 Since #31868 (Monaco → Shiki / `@pierre/diffs`), long lines on the template **Source Code** tab widen the content column past the page, which adds a page-level horizontal scrollbar. Monaco used to size itself to its container. The new renderer lays out real text, and the flex item had no `min-w-0`, so its min-content width was the longest line. Changes in `TemplateFiles.tsx`: - Add `min-w-0` to the content column, so long lines scroll inside each code block instead of widening the page. - Add `max-h-[calc(100vh-8rem)]` to the sticky file tree (`top-28` offset + 1rem), so `overflow-auto` takes effect and long trees stay inside the viewport. This is an older, related gap. Not changed: when the mouse wheel reaches the end of a code block, the page scrolls. `overscroll-contain` on the `SyntaxHighlighter` wrapper would stop this, but it is out of scope here. **Testing:** Biome passes. Checked visually on a Vite dev server proxied to dogfood: - `j-agents-template` (long line in `main.tf`): no page-level horizontal scrollbar, and the code block scrolls horizontally on its own. - `j-personalize-pr-1247`: the `main.tf` card fits the page and the **Edit** link is visible. - `j-filetree-overflow-test` (100 files): the file tree stays inside the viewport and scrolls on its own. <!-- screenshot: j-personalize-pr-1247 main.tf card fits the page --> <!-- screenshot: fixed file tree with its own scrollbar --> <details> <summary>Investigation notes</summary> - The layout classes (`flex items-start gap-8`, `flex flex-1 flex-col`) date to #12000 / #22369. The sticky tree dates to #26907. #31884, #31891, #31888, and #31890 only renamed or removed classes. - #31868 removed the JS-computed Monaco height (`min(lines × 18, 560)`) and replaced it with `max-h-140 overflow-auto` plus `overflow: "scroll"` on the renderer. This is where line width began to affect the layout. </details> --- <img width="3456" height="2062" alt="image" src="https://github.com/user-attachments/assets/70419de2-1fa6-4406-af40-28410d5ae996" /> <img width="1728" height="1035" alt="image" src="https://github.com/user-attachments/assets/c29d2eb0-fa52-4f09-a4f3-62cdf32deb32" /> _Generated by Coder Agents on behalf of @35C4n0r._ |
||
|
Nick Vigilante
|
6e2ff20d00 | docs: document patch release and backport policy (#31993) | ||
|
Ethan
|
3795d72713 |
fix: search AI Gateway models and clients by substring (#32159)
Closes AIGOV-801 Typing `hai` into the model filter on the AI Gateway sessions page shows the haiku models for a moment, then "No models found". Whilst the debounced request is pending, the menu filters the options it already has by a case-insensitive substring, but `GET /api/v2/ai-gateway/models` only matched a case-sensitive prefix, and Bedrock identifiers start with `anthropic.`. The client filter matched the same way, so it had the same problem. To fix, both endpoints now match a case-insensitive substring. This needed one change to the model menu. When the page loads with a model already in the filter, the menu used to look that model up on the server, by searching for its name and taking the first result. That's the same pattern as the user filter, where the lookup fetches the avatar, but a model option needs nothing from the server, so all it did was check that the model exists. With a substring search, the first result for `claude-3-5-sonnet-20241022` can be `anthropic.claude-3-5-sonnet-20241022-v2:0`, so the check would fail for a model that does exist. The menu now skips the lookup and just shows the model from the filter as selected. The only visible difference is that a model name in the URL that doesn't exist now shows as selected, instead of "All models". The client menu has the same lookup, which still works, as no client name contains another, so I've left it alone. The prefix match was added in #22230 (models) and #22694 (clients) so the queries could use the B-tree indexes. That only works on a C collation database, and only for models, as the clients query wraps the column in `COALESCE`. On an `en_US.utf8` database it's a plain filter either way. On a C collation database a model search with no matches does get slower, from instant to a few seconds with 5M synthetic rows, but I think that's worth it for a search that works. |
||
|
Kyle CarberryandClaude Opus 5.5
|
8922988e34 |
ci: stop auto-approving Dependabot PRs (#32303)
Removes the step that approved Dependabot PRs with `GITHUB_TOKEN`. Auto-merge stays enabled, so a Dependabot PR merges as soon as a person approves it and checks pass. The approval came from `GITHUB_TOKEN`, so it met the one-review rule on `main` without anyone looking at the dependency update. The org is turning off "Allow GitHub Actions to create and approve pull requests", which would make the step fail anyway. From now on Dependabot PRs need a human approval like every other PR. 🤖 Generated with [Claude Code](https://claude.com/claude-code) Co-authored-by: Claude Opus 5.5 <noreply@anthropic.com> |









